How American Interiors Removed Widespread Local Admin Rights
Discover how American Interiors eliminated local admin rights and enhanced security with ThreatLocker, transforming their IT management and troubleshooting processes.

What Was Found When Security Leaders Were Asked About Actual AI Adoption
Security leaders are cautiously optimistic about AI, seeking proven value and practical applications while prioritizing human oversight in automation.

When the Vendor Walks Away: Securing Software Nobody's Patching Anymore
Discover how organizations can secure outdated software when vendors stop providing patches, and the importance of visibility and extended support in managing legacy systems.

The AI Catastrophe Debate Is No Longer Theoretical
The debate on AI risks intensifies as capabilities outpace governance. This in-depth article explores the implications and necessary safeguards for advanced AI systems.

INFOGRAPHIC - Why Endpoint Security Must Go Beyond EDR in the AI Era
Discover key insights from our recent fireside chat on redefining endpoint security for the AI era, focusing on prevention and effective risk management.

Why Vulnerability Backlogs Are More Dangerous in the AI Era
In the AI era, vulnerability backlogs pose greater risks as machines exploit weaknesses quickly. Discover how AI-driven defense can reshape security strategies.

Defending Against the Risk of Weaponized AI
Discover how weaponized AI transforms cybersecurity threats and learn essential strategies for organizations to defend against evolving machine-based attacks.
AI and Endpoint Security, Prevention is the Path Forward
Find out how AI is reshaping endpoint security and discover the balance between innovation and risk management within cybersecurity.
INFOGRAPHIC: Mythos and What CISOs Need to Do Next
This infographic highlights key insights from our recent fireside chat on the most recent releases of AI's impact on cybersecurity and discover essential steps CISOs should take in response.
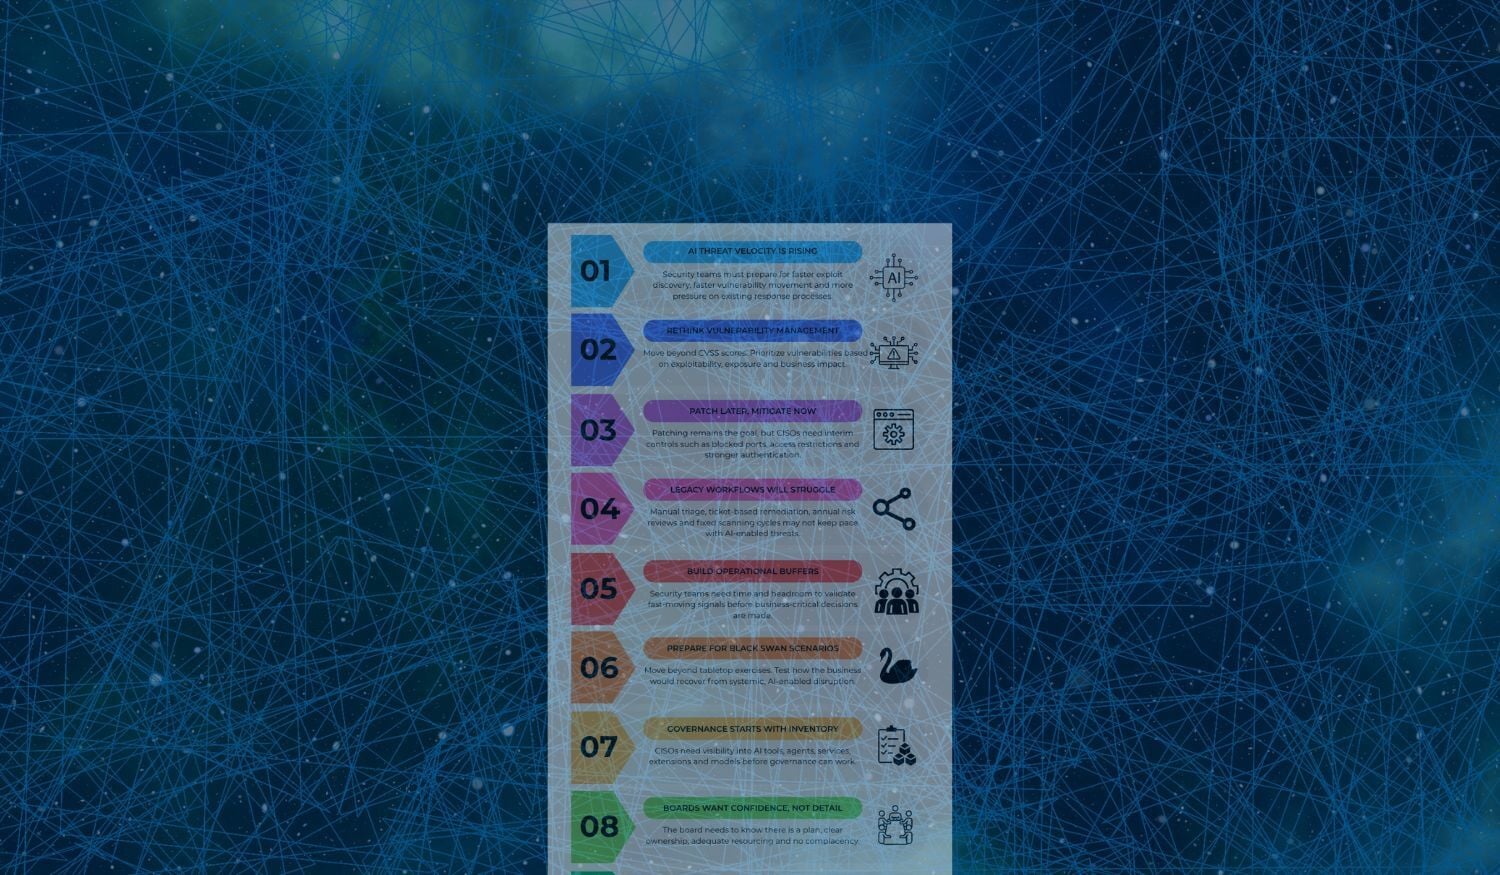
Closing the Gap Between AI Policy and AI Reality
This article explores how organizations can bridge the gap between AI policy and actual usage, ensuring safe, visible, and governed AI interactions in the workplace.