
Third-Party Risk Management (TPRM) is not new discussion; it’s been a topic as long as I can remember and as long as I’ve been doing this (that’s a long time!). But it’s evolving. The concerns today are being amplified by AI, specifically when vendors add AI into their solutions after contracts have been signed. Fourth-party risk has also become increasingly important because, of course, every vendor has vendors of their own.
A CISO recently asked “Is any of our third-party risk management even effective? Why do we do this? Should we just focus on our defenses more?” I understand the thinking behind his question, but organizations still need a strong TPRM process. The real question is whether the process that’s been relied on for years is still the right one. I had an opportunity to speak with Rich Latayan, CISO, AAA to discuss how TPRM should be approached today, including the onboarding of new vendors and continually reviewing the vendors already in your environment.
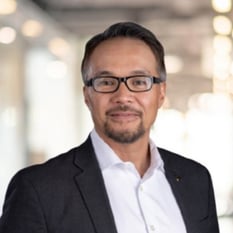
Rich Latayan, CISO, AAA
Q1. When you look at third-party risk today, what has changed most compared with three or four years ago?
Rich Latayan: Definitely the speed. The rate of change in the industry. With third parties it boils down to nothing is point in time anymore because of the rate of speed, so you really do have to look from the lifecycle. It's not just at the point of onboarding that you need to focus on. It's throughout the engagement as well as at the end of any engagement with the third party. I think our ability to be able to look at the whole lifecycle and the spectrum at a much quicker pace is really important.
Q2. Organizations are relying on an ever-growing ecosystem of vendors, SaaS platforms and service providers. How do you determine which third parties deserve the greatest scrutiny? Are there some that require more scrutiny than others?
Rich Latayan: Yes, there are. It's common practice to look at priorities, tiering models, and the level of impact in terms of measuring it within your organization. You need to apply traditional risk management practices and enterprise risk management practices; those are really good because you need to be able to factor in the impact of that vendor to your operations. They stem from financial to outages and availability, and for them to provide you the continuity in your business processes, because they are really integral to everything that we do. No one does anything by themselves anymore, and so I think that it's important to look at that and have a prioritized risk tiering model that evaluates and assesses the risk of third parties, respectively. The more risky the vendors are, the more intense scrutiny they should go through.
Q3. When you look at traditional third-party risk management, where are those programs falling short? Are there practices organizations rely on that no longer give you, as a CISO, the visibility or assurance you need?
Rich Latayan: The static review assessment no longer applies, because you can't just review a vendor onboarding, sign some contracts, and then wait until an incident happens. It has to be a true partnership from the get-go, understanding the impact level and then factoring in some signals and rhythm to your cadence for reviews. I find that sometimes there's fragmentation with the different businesses and practices within an organization. So if it's your procurement, your security, your IT, the business lines, they all have to be embedded into the overall TPRM, Third-Party Risk Management Program.
Q4. How do you move beyond assessing a vendor at onboarding and get meaningful visibility into how that vendor's risk changes over the course of the relationship?
Rich Latayan: That's where the lifecycle is really important. I call it triggers and signals. You need to be able to have these markers in terms of if new data elements are introduced, if there's new integration, AI, there's always a new functionality. You can't wait until you hear about these things; you have to be really proactive. Most organizations by now have a security operations center, and that's centered around threat intel. So it's more than the dialogue with the vendors, which is really important, but relying on other sources, whether it's the dark web or indicators of compromise that are all in the industry. You need to be able to bring that in to your overall lifecycle review of a vendor or third party.
Q5. How has AI changed the third-party risk conversation, particularly when vendors introduce AI capabilities, models or data dependencies that weren't part of the original evaluation?
Rich Latayan: There's a little shift now because a couple years ago, we weren't looking at agents, let alone these types of models. While data is still principle to a lot of things, access is very important. Those are the principles, but now we're asking the questions around models. What is an AI agent doing? What can it do? What are the parameters that you've put in place? I think the growing practice around AI governance gates is very important, because you need to be able to understand the usage of your own data, or how they plan to use it, and have all the guardrails in place, not only from a regulatory standpoint, but a privacy standpoint as well. At the end of the day, we're all in it together, and those governing practices need to carry out throughout the engagement of the supply chain.
Q6. Looking at AI, there are two pieces: the questions you ask new vendors you're onboarding and the vendors you've already had in place that are suddenly using agents or other AI capabilities they didn't have before. Are you going back to those existing vendors, and are there different questions you're asking new ones?
Rich Latayan: You have to go back. When we look at some of our key partners from a lifecycle perspective and a tiering model, contracts that were initiated a couple years ago will not have the AI language. Developing the standards for AI in terms of third parties, and there's many references out there such as NIST and CSF, incorporating those into the new engagement, but going back to each and every vendor is important. It’s time-consuming, but it's worth the effort. Again, looking at tiered models, the ones that are risky and most important, and rewrite some of the contracts. In fact, we've taken the approach to writing data privacy and security standards specific to AI, so there are a set of obligations that are now passed through attorneys to be incorporated into all contracts.
Q7. How frequently do you go back and review those contracts?
Rich Latayan: They need to be annually, because things change so much, and going through the older engagements we can see where the cracks lie. So, as frequent as you can. Again, I'm going to go back to the tiered model: your most sensitive and impactful vendors, probably once a year would be ideal.
Q8. One of the challenges with third-party risk is that security doesn't necessarily own the vendor relationship. How do you effectively engage procurement, legal and the business without being the team that simply says no?
Rich Latayan: The good and bad side of things, and why I enjoy security so much is because we do span a lot of different business units. But I see it as a four-legged stool, in the sense that there's four key elements. For procurement, we need their help and they can leverage different things in terms of what needs to be put into their organizations. Legal, I call the hammer, or the enforcer and once things are established, we lean towards them and their ability to enforce the contracts. And then, of course, the business provides us the context; what are we really protecting of the processes and data? We lean on them to help. Finally, the information security team: we need to be able to provide the visibility into the risk, and that's what I think it's all about. We need to be business partners to all the varying business units within an organization to make this all work.
Q9. How do you think about fourth-party or concentration risk, where several critical vendors may ultimately depend on the same cloud provider, technology platform or underlying service?
Rich Latayan: You need to start now. We always talk about third parties, and fourth becomes just something in the background, but everyone relies on everyone else. No one's storing really any of this information within their own four walls, it all comes down to the cloud providers. You’ve got the major providers, the data warehouses and you need to gain some assertions around the security of those practices through your third party. It’s becoming even more important now because data could live anywhere, and the speed in which they're transferred means you need to be able to understand the dependencies around that. Risk is just amplified when it's downstream into the fourth party. So, again, being able to understand who they are, accountability on that, and then the levels of protections that they have in place for the fourth parties.
Q10. When a critical third party experiences a security incident, what's the best practice?
Rich Latayan: I would say that if you're trying to figure this out afterwards, it's too late. So when we talk about onboarding and signing contracts, a lot of this really should be discussed in terms of the playbooks. There should be a collaboration around the playbooks and how to respond. I think the industry has come to terms around assuming breach is imminent, and that's how you should think about your third parties. It's not if, it's really when. We all do our tabletop exercises, and I find that companies are now starting to include the third party into the simulations. Few, if any, do any kind of processing, storage, etc. We really rely on our third parties in the entire supply chain. It’s important to have those discussions, and to a degree within the contract obligations, in terms of how security incidents are handled.
Q11. If another CISO asked you where they should focus their third-party risk efforts over the next 12 to 24 months, what would you tell them?
Rich Latayan:
- There's something to be said about prioritizing tiering, because for large organizations, you'll have thousands of vendors, and we don't exactly have all the resources. It's not unlimited.
- Signals and triggers. You need to customize what that looks like for each third party you leverage, because there might be some indicators there that may spawn other reviews or other questions you may have for that particular partner.
- We talked about the fourth parties. You need to map them out now, and then connect the dots around where they are most critical to your business and how you're going to address them.
- Take a look at their AI practices. What is their AI culture like? Does it resonate with yours?
- Sharing the governance framework is very important, because at the end of the day, we're all trusted companies, and we need to ensure that we have the proper governance protection to ensure that we are trusted.
Q12. Anything we didn't touch on that you were hoping to cover on the third-party risk piece?
Rich Latayan: The one thing I would say is that we like to say that compliance is the floor, not the ceiling, but very important. You could always lean on other regulations, because we hear about DORA in terms of how they're looking at more of the dependencies around third party. You look at banking and they are focused around the fact that you just can’t transfer risk, and I think that applies to everyone. The SEC has rules around disclosures. The back end of that is no one wants to be scrutinized after an incident. It’s important that we all front-load our efforts, so that the back end isn't as critical, or we don't get caught in certain circumstances that we don't want to be in.
Addressing CISO Challenges, RSAC 2025 Vendors
How Organizations Can Utilize Cybersecurity Start-up Vendors